Posts

What should you know about CISCO’s high-severity zero-day vulnerabilities?

Image
  CVE 2023-20198 – CISCO’s maximum severity zero-day vulnerabilities Cisco has issued an alert over its critical zero-day vulnerability detected in their IOS XE software range. The vulnerability is targeted toward systems that have HTTP/HTTP servers turned on. More than 40000 Cisco devices are now affected by this vulnerability, with 10,000 Cisco devices found with an implant for arbitrary code execution. The critical vulnerability CVE-2023-20198 is assigned a severity rating of 10. That is the highest rating given on a CVSS vulnerability severity scale. It is present in the Web UI component of IOS XE software. This vulnerability allows privilege escalation that enables an attacker to gain a full takeover of the system in that he has implanted the malware to. It means that cyber attackers can exploit this vulnerability to hijack a CISCO router and gain control of it. The countries that are impacted the most by this vulnerability include the US, the Philippines, Mexico,...

24/7 SOC as a service | SharkStriker

Image
  Gain round the clock comprehensive security from a team of cybersecurity analysts and cyber security experts with SharkStriker’s SOC as a service. A 24/7/365 Security Operations Center (SOC) is crucial for several reasons: Continuous Threat Monitoring: Cyber threats can occur at any time, day or night. Having a SOC that operates around the clock ensures that potential threats are identified and addressed promptly, reducing the risk of a successful attack. Swift Incident Response: In the event of a security incident, time is of the essence. A 24/7 SOC allows for immediate response to breaches, minimizing damage and preventing further compromise. Global Reach and Coverage: Cyberattacks are not confined to specific time zones or regions. Having a SOC that operates continuously ensures that your organization is protected regardless of its geographical location. Real-Time Threat Intelligence: The cybersecurity landscape is constantly evolving. A SOC that operates 24/7 can monitor ...

SIEM as a service by sharkstriker

Image
  Hunt and avert threats before they haunt you with a human-led tech-driven solution that gives you 360-degree visibility, continuous monitoring, and compliance management all from a single platform STRIEGO. Gain the freedom to choose with predictable asset-based pricing and cloud/on-premise deployment. SIEM (Security Information and Event Management) as a service is a cloud-based solution that offers a centralized platform for monitoring and managing an organization's security events and incidents. Here are several ways SIEM as a service can benefit your organization: 1. Real-time Threat Detection: SIEM tools continuously monitor network traffic and log data in real time. They can quickly identify and alert on suspicious activities or security incidents, allowing for a rapid response. 2. Improved Incident Response: SIEM solutions provide a comprehensive view of security events, allowing your security team to investigate and respond to incidents more effectively. This can lead to ...

Critical CVIS 10-rated Zero-day Webp vulnerability wildly exploited. Reassigned to CVE-2023-5129.

Image
Google’s libwebp based zero-day vulnerability is now reassigned to CVE 2023-5129. It is wildly exploited. Attackers are using webp images to transmit malicious codes to extract sensitive information from their victims.  Google released a security fix for a critical vulnerability that affected Google Chrome for Windows, macOS, and Linux. The vulnerability was given the CVE ID as CVE-2023-4863 and has been given a severity of 8.8 (High). On analyzing the vulnerability, it was discovered that a heap buffer overflow vulnerability existed in the libwebp library that a threat actor can exploit to perform out-of-bounds memory write via a crafted HTML page. However, this vulnerability was resubmitted by Google, which is now tracked as CVE-2023-5129. It was later found that CVE-2023-41064 and this vulnerability were similar and affected the same libwebp library.   Threat actors exploited this particular library during the BLASTPASS exploit chain attack for deploying the NSO’s Pega...

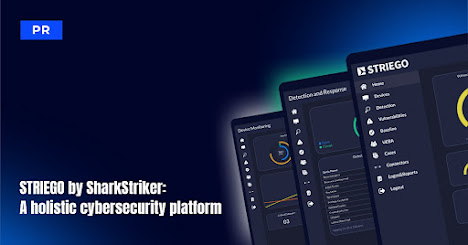
STRIEGO by SharkStriker: A holistic cybersecurity platform

Image
A unified multi-tenant open architecture human-led AI/ML-driven security platform designed to meet the cybersecurity needs of today and tomorrow.   SharkStriker Striego is a multi-tenant, open-architecture, human-led AI/ML-driven security platform designed to solve the most immediate challenges in cybersecurity and compliance. It helps organizations by providing them with a single stop for all their cybersecurity and compliance needs. It is managed by a dedicated team that can implement the best practices in the industry, helping businesses make the most of their existing cybersecurity investments. As businesses worldwide increase their demand for enterprise-grade security, they are faced with an increased challenge of aspects of cybersecurity being highly siloed off, a limited team for cybersecurity, and the rising cost of cybersecurity solutions. To solve this challenge, SharkStriker has come up with a holistic cybersecurity platform - STRIEGO, that not only seamlessly integra...
Image
What is Incident Response? why do organizations need it?  Incident response comprises all the security measures taken to detect, respond and contain a cyber incident such as data breach or a ransomware attack.   Incident Response (IR) is a structured approach used by organizations to address and manage the aftermath of a cybersecurity incident. A cybersecurity incident refers to any event that poses a threat to the security of an organization's information systems, networks, or data. These incidents can range from malware infections and data breaches to denial-of-service attacks and insider threats. Here are the key components of an Incident Response process: Preparation: This phase involves setting up the necessary policies, procedures, and resources for effective incident handling. It includes tasks such as creating an incident response plan, defining roles and responsibilities, and establishing communication channels. Identification: In this phase, organizations work to ...
Image
  What is Whaling attacks? how to prevent them | SharkStriker Whaling attacks are a kind of phishing attacks aimed towards the top management executives. Safeguard your email by double checking them for syntax, mail protection software etc. A whaling attack, also known as a whaling phishing attack or a CEO fraud, is a highly targeted form of phishing attack that specifically targets high-profile individuals within an organization, such as executives, high-ranking officials, or other individuals with significant decision-making authority. The term "whaling" is used because the attackers are "harpooning" the "big fish" in the organization. In a whaling attack, the attacker typically poses as a trusted entity, often using email or other electronic communication methods, and attempts to deceive the target into taking a specific action. This action might involve providing sensitive information (such as login credentials or financial details), transferring fun...